Continuous security for everySolana deployment
Monitor executable bytes, ProgramData, deployment slots, upgrade authority, IDLs, and source references. UseKratose turns every observed change into deterministic, reviewable security evidence.
Certificate transparency and Git-style security diffs for deployed Solana programs.
Continuous security coverage for deployed Solana programs
Observe what is on-chain, preserve every version, and explain exactly what changed without inventing findings.
Deployment fingerprints
Hash executable bytes and canonical loader state so every observed deployment has a reproducible identity.

Deterministic evidence
Upgrade detection
Pair WebSocket monitoring with reconciliation polling so disconnects never silently erase an upgrade.

Deterministic evidence
Authority intelligence
Track upgrade authority, immutability, owner, and ProgramData transitions with explicit evidence.

Deterministic evidence
IDL-level diffs
Reveal instruction, signer, writable-account, argument, account-type, and error-definition changes.

Deterministic evidence
Verification staleness
Automatically mark a previously trusted fingerprint stale when the deployed program no longer matches it.
Deterministic evidence
Explainable events
Use fixed security rules and structured evidence instead of opaque numerical scores or AI-generated findings.
Deterministic evidence
From on-chain observation to an explainable security event
Every stage preserves provenance, remains deterministic, and degrades gracefully when optional metadata is unavailable.
Observe deployed truth
Establish a finalized baseline directly from Solana RPC before drawing any conclusion.

Executable fingerprint and deployment slot
ProgramData and upgrade authority
IDL, instruction, account, and source changes
 Verifying finalized deployment evidence
Compare consecutive versions
Detect executable, slot, authority, ownership, ProgramData, IDL, instruction, and source-reference changes from stored snapshots.
Deliver structured evidence
Persist deduplicated security events, mark stale verification, notify teams, and expose the exact transition through the API and dashboard.


just now

Useful for every program. Richer when metadata exists.
UseKratose never pretends optional IDL or source evidence is universal. Each layer clearly states what was observed and what remains unavailable.
On-chain evidence
The deterministic baseline available for every supported Solana loader-v3 program.
Program and ProgramData resolution
Executable SHA-256 deployment fingerprint
Deployment slot, owner, and upgrade authority
Program intelligence
Deeper interface and provenance context whenever authoritative metadata exists.
Normalized IDL fingerprint and structured diff
Instruction, signer, writable-account, and schema changes
Repository revision and source-verification state
Security operations
Operational delivery for teams that need continuous evidence after every deployment.
Deduplicated security-event ledger
Alert destinations and project-scoped API access
Human-readable evidence with optional AI explanation

Built in verifiable layers, not feature theater
Each shipped layer is validated before the next one becomes part of the product surface.

Continuous program monitoring
Resolve loader-v3 ProgramData, fingerprint executable bytes, extract authorities, and combine WebSocket signals with reconciliation polling.
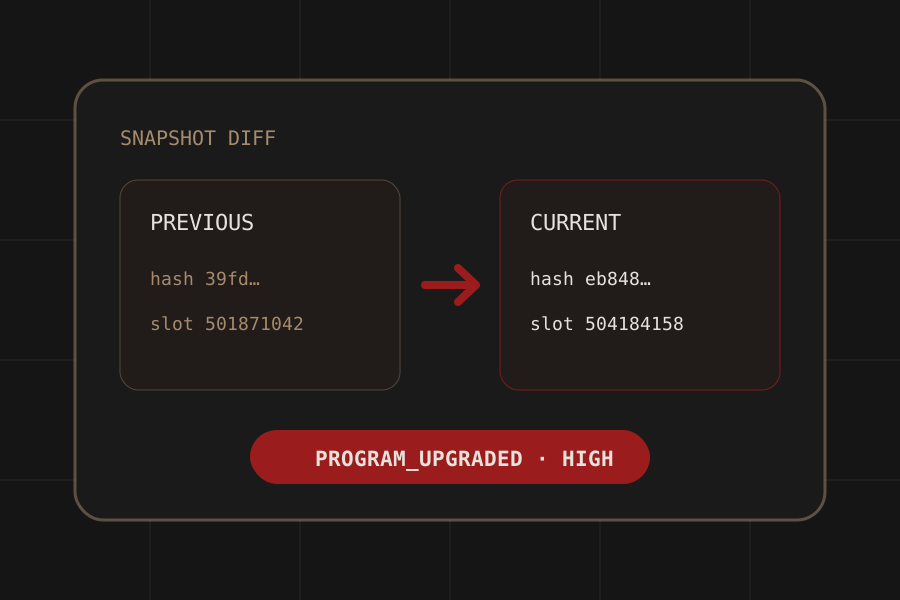
Deterministic security events
Compare consecutive snapshots and persist explainable events for upgrades, ownership, authority, IDL, instruction, and verification changes.
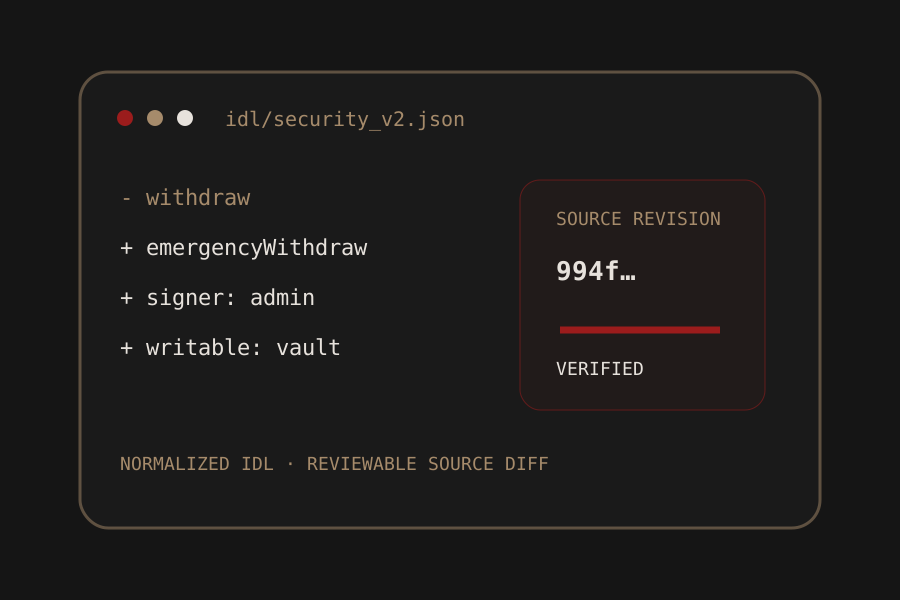
IDL and source intelligence
Normalize available IDLs, identify schema-level deltas, preserve verified repository references, and degrade gracefully when metadata is unavailable.

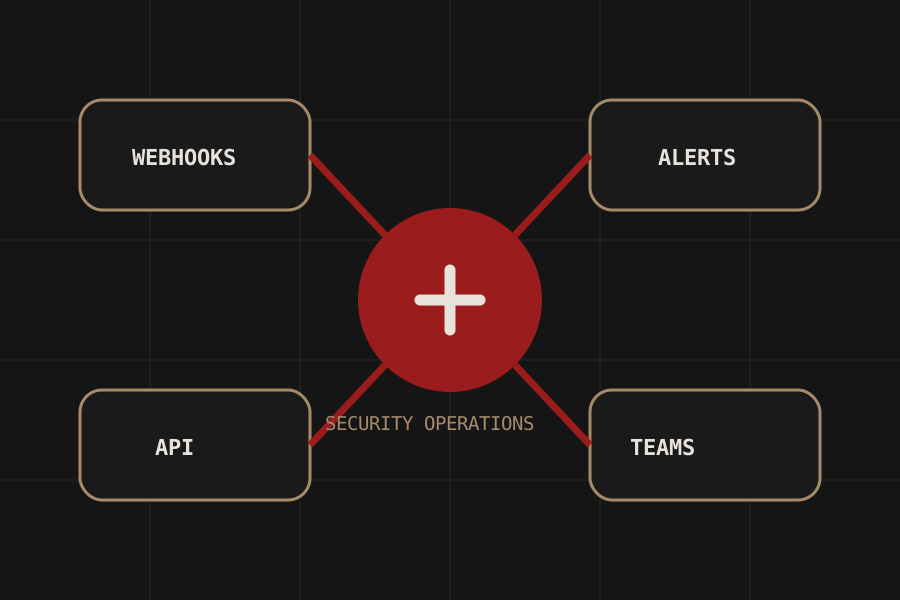
Protocol operations
Expand delivery workflows, webhook automation, public API ergonomics, and onboarding for real Solana protocol security teams.